

Technology investments in most organizations advance as a series of disconnected decisions. One year the firewall is replaced, the next year the backup solution changes, the year after that a monitoring tool is deployed. Each step is sound on its own; yet the sum of those steps rarely amounts to an enterprise IT infrastructure strategy. What emerges instead is a collection of products that do not know one another, in a structure no single party owns end to end.
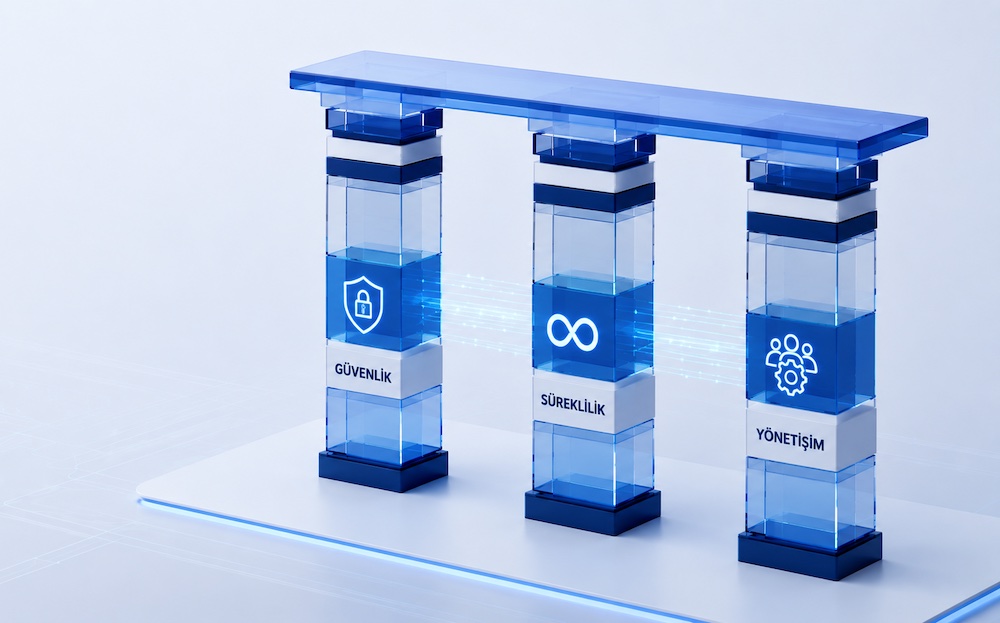
A healthy IT infrastructure, by contrast, rests on three pillars: security, continuity and governance. If any one of them is missing, the structure will not hold no matter how strong the other two are. In this series, which begins with this article, we will address these three pillars and the technical topics beneath each of them in turn. Let us start by setting the framework.
Why Three Pillars?
An IT infrastructure has to answer three distinct questions, and none of them substitutes for another:
- How do we prevent unauthorized access? This is the question of security.
- What happens when something breaks? This is the question of continuity.
- Who manages what, and against which criteria? This is the question of governance.
Most organizations invest in the first question, prepare partially for the second, and often never ask the third. As a result, we encounter organizations that own capable security products yet cannot say who holds which privileges, or whose backup system runs reliably but whose recovery time has never been measured. The problem is not budget; it is the absence of a framework.
First Pillar: Security
Security is no longer a matter confined to perimeter defence. Being inside the corporate network does not make a user trustworthy. The modern approach rests on an architecture that verifies every access request independently of its origin. Zero Trust architecture, the expression of that approach, is a topic we will examine in detail in a forthcoming article.
The core areas covered by this pillar are:
- Identity and access management: Multi-factor authentication, role-based authorization and regular privilege reviews.
- Network segmentation: Logical division of the network so that an attacker who breaches one point cannot move laterally.
- Endpoint and server protection: Behaviour-based detection, current patch management and centralized visibility.
- Encryption: Protecting data both at rest and in transit.
- Detection and response capability: How quickly an incident is noticed matters as much as whether it was prevented.
The real measure of the security pillar is not which products you own, but how many steps it takes to stop an attack scenario.
Second Pillar: Continuity
Continuity means that the business keeps running when something goes wrong. Where security focuses on prevention, continuity manages what could not be prevented. Hardware failure, a data centre outage, human error or a successful ransomware attack — every one of these scenarios is measured by how quickly the organization gets back on its feet.
The components of this pillar form a layered structure:
- Redundancy: Eliminating single points of failure through duplication at the power, network and hardware levels.
- High availability (HA): Keeping the service running without interruption when a component goes offline.
- Backup: The 3-2-1 rule and immutable copies that resist ransomware.
- Disaster recovery: RPO and RTO targets defined together with business units and validated through regular drills.
We covered the storage-side counterpart of these topics in our earlier article, How Secure Is Your Data? Enterprise Storage Strategies. The golden rule of the continuity pillar is simple: an untested recovery plan is not a plan.
Third Pillar: Governance
This is the most neglected pillar, because there is no product you can purchase for it. Governance defines who manages the infrastructure, under which rules, and against which measures. An inventory that is out of date, a server whose purpose nobody remembers, a project left unowned after go-live — all of these are governance failures.
The essential elements of this pillar:
- Inventory and configuration management: Nothing can be managed without knowing what exists and where.
- Change management: A significant share of outages stems not from attacks but from uncontrolled change.
- Monitoring and reporting: An infrastructure that is not measured cannot be improved.
- Documentation and knowledge continuity: Keeping knowledge within the organization rather than within individuals.
- Compliance: Reflecting KVKK (Turkey's Personal Data Protection Law) and sector-specific regulations in infrastructure decisions.
We detailed our approach to the post-deployment phase of projects in The Importance of the Right Methodology in IT Projects.
How the Three Pillars Support One Another
These pillars do not operate independently; weakness in one renders another ineffective. A few examples make this concrete:
- If you have backups but they are not immutable, ransomware brings down continuity by way of security.
- If your security products are strong but your inventory is incomplete, you remain unaware of the systems you are failing to protect.
- If you have a high-availability design but no change management, the outage will be caused not by a fault but by a misconfiguration.
Infrastructure investments should therefore be evaluated not as isolated product decisions, but as a whole that keeps the three pillars in balance.
Six Questions to Assess Your Organization
- Can a user already inside your network reach critical systems without further verification? If yes, the security pillar has stopped at perimeter defence.
- When did you last perform a restore test? If the date cannot be recalled, recovery capability has never been measured.
- Can you state how many servers you have from a single source? A scattered inventory points to a gap in governance.
- Who makes configuration changes, and under whose approval? Without a defined process, the risk is operational in origin.
- Were your RPO and RTO targets defined together with business units? Targets set by the IT team alone may not reflect business reality.
- When did you last assess your infrastructure as a whole? Piecemeal renewal does not strengthen the whole.
If several of these questions cannot be answered clearly, the issue is usually not a lack of technology, but an imbalance among the three pillars.
The ORBISIS Approach: The Whole, Not the Product
At ORBISIS we approach infrastructure projects through all three pillars rather than through a single component. Across the projects we have delivered for public and private sector clients since 2013, we always begin with an assessment of the current state, identify which pillar is weak, and direct the investment to the point where it will genuinely pay off. Our responsibility does not end at installation; we continue to follow the monitoring, maintenance and improvement processes.
In the coming weeks this series will deepen the security pillar with articles on AI-driven cyber security and Zero Trust architecture, followed by dedicated articles on the continuity and governance pillars.
To assess your organization's IT infrastructure across these three pillars together, explore our Assessment Services and Data Center and Infrastructure Solutions pages, or get in touch with our expert team.